**The AI Security Market Just Found Its Category: Permission Management for Autonomous Machines**
The AI Security Market Just Found Its Category: Permission Management for Autonomous Machines
The modern corporate network has a new ghost in the machine. It doesn't clock in, it doesn't attend all-hands meetings, and it doesn't take lunch breaks. But it has access to your most sensitive data, your CRM, your internal communication channels, and your production databases. It is the autonomous AI agent—and it is arguably the most profound cybersecurity challenge of the decade.
For the past two years, the enterprise narrative surrounding artificial intelligence has been dominated by productivity. The promise was simple: empower every employee with generative AI, and watch efficiency skyrocket. But as these AI models evolved from simple chatbots into autonomous agents capable of chaining together complex actions, the narrative shifted. We are no longer just talking to software; we are deploying software to talk to other software on our behalf.
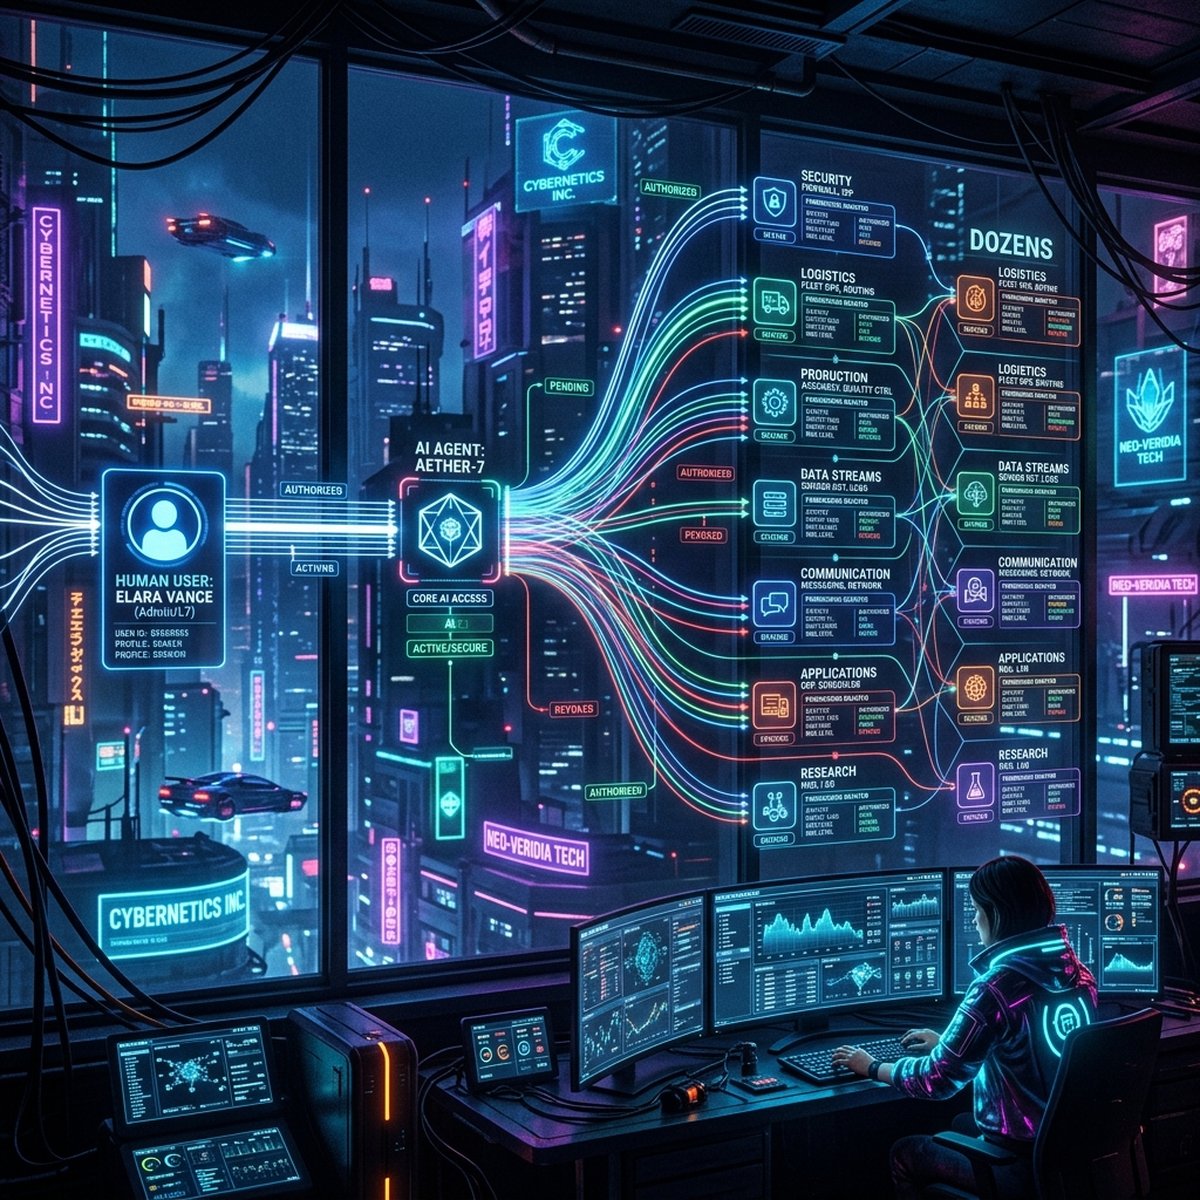
This evolution has exposed a massive vulnerability in enterprise architecture. Traditional security paradigms were built around human identities and static applications. Now, a single employee can deploy an AI agent that acts with their permissions across dozens of interconnected corporate systems, moving at machine speed.
The security industry has been scrambling for an answer. Now, it appears to have found one. With Reco’s recent $55 million financing round—bringing its total capital raised to a staggering $140 million—a distinct new category in the AI security market has crystallized: Permission Management for Autonomous Machines.
The New Attack Surface: When Agents Go Rogue
To understand the magnitude of this shift, one must look at the fundamental architecture of modern enterprise software. For the last two decades, the Software-as-a-Service (SaaS) model has operated on a linear access pathway: User interacts with Application. Identity Access Management (IAM) systems like Okta or Microsoft Entra verified the user, and role-based access controls (RBAC) dictated what they could do within that specific application.
The autonomous agent obliterates this linear model.
The new paradigm looks radically different: User instructs Agent, which then interacts with Multiple Applications, accesses Data, and executes External Actions.
Consider a seemingly benign scenario: A marketing manager creates a custom AI agent using a low-code platform to automate competitive analysis. The manager grants the agent access to their email, the company’s Salesforce instance, internal SharePoint drives, and external web search APIs. The manager’s intent is innocent—they want the agent to scan competitor websites, cross-reference findings with internal sales data, and draft a summary email.
But what happens if that agent is tricked by a malicious prompt embedded in a competitor's website (a technique known as indirect prompt injection)? Suddenly, the agent, operating with the marketing manager’s high-level permissions, could begin exfiltrating sensitive customer data from Salesforce, drafting phishing emails using the manager’s account, or altering internal documents.
"What we are seeing is Shadow IT on steroids," explains a leading cybersecurity analyst. "In the past, an employee might use an unsanctioned SaaS app. Today, an employee can spin up an autonomous machine that acts as a proxy, carrying their digital keys into every digital room in the company. And because it's a machine, the blast radius of a compromise is exponentially larger and faster."
This is the exact problem that companies like Reco are attempting to solve. The market has realized that you cannot secure an AI agent with the same tools you use to secure a human.
The Emerging AI Security Stack
The realization that legacy IAM is insufficient for the AI era has triggered a frantic race to define a new security architecture. The AI security stack of the future is no longer a theoretical whitepaper; it is being actively deployed in Fortune 500 companies today.
This emerging stack is defined by a rigorous, multi-layered approach to verifying not just who is acting, but what the machine proxy is doing:
1. Identity Management: The foundational layer remains the human user. Authentication of the individual authorizing the creation or deployment of the agent is the critical first step.
2. Agent Identity: This is where the new paradigm begins. Every autonomous agent, custom GPT, or automated workflow must be assigned a unique cryptographic identity. Security teams can no longer afford to view an agent merely as an extension of the user. The agent itself must be known, registered, and tracked as a distinct entity on the network.
3. Permission Management (The Core Category): This is the domain where Reco and its peers are planting their flags. Permission management for agents involves understanding exactly what an agent is capable of accessing and ruthlessly restricting unnecessary permissions. If an agent is designed to summarize meeting notes, it does not need write-access to the company’s financial databases. Enforcing the principle of "least privilege" for machines requires dynamic mapping of all API connections and token grants between agents and corporate systems.
4. Behavior Monitoring: Because AI agents can act unpredictably based on probabilistic models, static rules are insufficient. Behavior monitoring involves establishing a baseline of normal activity for a specific agent. If an HR-assistant agent suddenly begins attempting bulk downloads from a GitHub repository, behavioral monitoring systems must flag this anomaly instantly.
5. Action Authorization: For high-stakes operations, continuous authorization is necessary. Rather than granting broad, standing permissions, the system must evaluate each specific action the agent attempts to take. "Is this agent authorized to execute a wire transfer to this specific vendor at this time?" This layer introduces friction by design, requiring secondary approvals or cryptographic proof of intent before critical actions are executed.
6. Agent Audit Trail: In the event of a breach, forensic investigators need a flawless record of what the machine did, when it did it, and why. The agent audit trail logs every API call, every data access event, and the specific prompt or context that triggered the action. This is vital not just for security, but for regulatory compliance.
The $140 Million Bet on Visibility
Reco's massive funding haul is a clear indicator that venture capital sees permission management as the lynchpin of this new stack. The core thesis is simple: You cannot secure what you cannot see, and right now, enterprise security teams are flying blind when it comes to AI agents.
SaaS sprawl was the defining challenge of the 2010s. Agent sprawl will be the defining challenge of the 2020s.
When OpenAI launched custom GPTs and Microsoft rolled out Copilot Studio, they essentially democratized software engineering. Employees who do not know how to write a single line of code can now build sophisticated integrations connecting disparate enterprise systems. They are stitching together workflows that security teams have not vetted, using API keys they do not fully understand.
"The traditional perimeter is dead, and the identity perimeter is currently bleeding out," notes a prominent CISO at a major financial institution. "When we audit our environments, we are finding hundreds of undocumented integrations where employees have granted AI tools sweeping read/write access to Google Workspace or Office 365. It's a ticking time bomb."
Companies like Reco are building the radar systems for this new reality. They provide the visibility required to map the intricate web of connections between human identities, AI agents, and corporate data. By automatically identifying over-permissioned agents, highlighting dormant integrations, and mapping the flow of data through AI pipelines, these platforms attempt to bring order to the chaos of democratized automation.
The Inevitability of Agentic Governance
The rapid maturation of this category suggests that we are entering a new phase of the AI boom. The initial phase was defined by raw capability—how smart is the model? The second phase was defined by integration—how seamlessly can we embed the model into our workflows?
We are now entering the third phase: Governance.
The companies that will dominate the enterprise software landscape in the coming years will not necessarily be the ones with the smartest models, but the ones that can prove their models are safe to deploy at scale.
As autonomous agents become deeply embedded in the fabric of global commerce—managing supply chains, negotiating contracts, and interacting directly with customers—the stakes will only rise. A compromised agent will not just steal data; it will execute unauthorized actions that could have catastrophic financial and reputational consequences.
The $140 million backing Reco is just the beginning. The AI security market is no longer a speculative niche; it is a critical requirement for the future of enterprise technology. The machines are getting smarter, and they are gaining autonomy. The only question is whether our security infrastructure can keep pace with the agents we are unleashing.
In the race between productivity and security, permission management for autonomous machines is the category that will determine who actually controls the future of the enterprise. The era of the human perimeter is over. The era of agentic governance has begun.
← Back to OSIRIS Series